Authority chains will become machine-readable
As agents delegate subtasks to other agents, a simple user login cannot explain the full chain behind a consequential action.
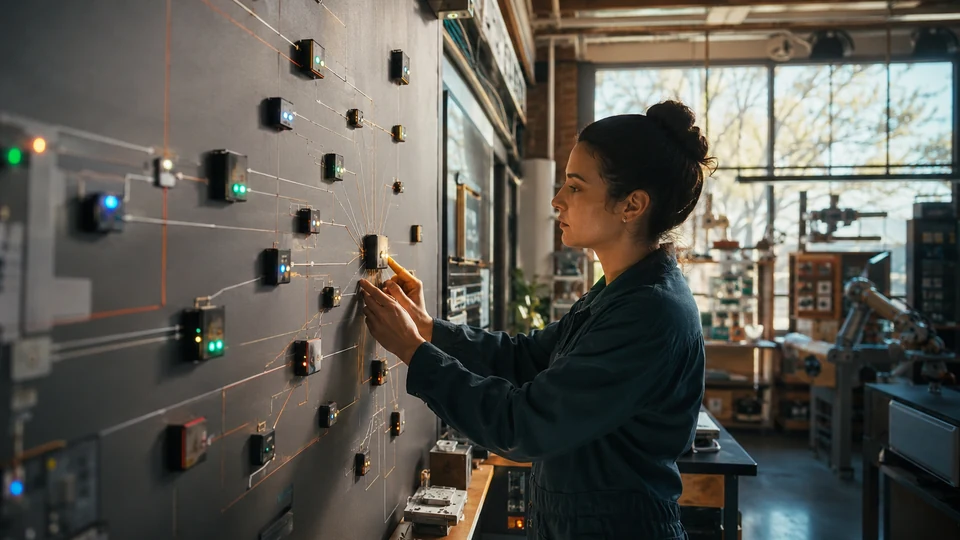 FUURAA original conceptual visual
What the evidence indicates
The Core Argument of “Accelerating the Adoption of Software and Artificial Intelligence Agent Identity and Authorization”
As agents delegate subtasks to other agents, a simple user login cannot explain the full chain behind a consequential action.
FUURAA Editorial Analysis
Reading “Software and AI Agent Identity and Authorization”: Can an Authority Chain Travel With Every Action?
As orchestrators delegate work to subagents and external tools, a final service needs to understand more than the first user login. It may need evidence of who initiated the task, which agent received authority, what portion was delegated onward, which policy applied and whether that authority remains valid. NIST’s draft identifies delegation, logging, non-repudiation and data provenance as connected questions. A machine-readable authority chain is a plausible architectural response, but it remains a FUURAA forecast rather than a NIST-mandated standard.
The Core Argument of “Software and AI Agent Identity and Authorization”
The concept paper links user identities to agents for delegation and accountability, asks how an agent proves authority for a specific action, and calls for verifiable logs that bind actions back to human authorization. It also proposes tracking prompt and data-source provenance to support policy decisions. Read together, these requirements imply that authorization evidence must move through an agentic workflow rather than remain only at the first gateway. The paper does not name a universal authority-chain format. It inventories relevant mechanisms—including OAuth, OpenID Connect, workload identity, lifecycle provisioning and policy-based control—and seeks evidence about how they can be combined in real enterprise architectures.
A useful chain records derivation, not every internal detail
An authority chain should identify the initiating principal, each delegating and receiving non-human identity, the purpose and permitted action, policy and credential versions, scope reductions, expiry, revocation status and the final relying service. Each hop should be able to prove that it received no more authority than its parent possessed. The record need not expose hidden model reasoning or copy all private data. It should preserve decision-relevant facts and hashes or references to protected evidence. Selective disclosure is essential: a downstream service may need proof that a payment ceiling was approved without learning unrelated user attributes or the entire conversation.
Nested delegation creates attenuation and revocation problems
When one agent creates a specialist sub-task, authority should normally narrow rather than expand. A research subagent may read approved sources but should not inherit permission to send email; a deployment worker may act on one repository and environment but not every account the orchestrator can reach. Chains therefore need attenuation rules, audience restrictions and maximum depth or time. Revocation is harder: cached credentials, queued work and offline tools may continue after the root grant is withdrawn. Robust designs should use short-lived capability, online policy checks for consequential actions and a mechanism to invalidate descendants. Failure to propagate revocation should be visible as an incident, not silently accepted.
Audit evidence must be trustworthy without becoming surveillance
Tamper-evident records can improve non-repudiation and incident response, but logging every prompt, document and intermediate output can create a new concentration of personal and commercial data. Organisations should define the minimum evidence needed for accountability, separate operational logs from sensitive content, encrypt and limit access, apply retention schedules and record when evidence is disclosed. Clock synchronization, stable identifiers and signed policy decisions matter because a chain assembled after an incident is weaker than evidence produced during action. Human override should also be represented: a reviewer’s approval, rejection or modification becomes another bounded delegation event, not an unexplained break in the record.
Evidence that should strengthen or weaken the forecast
The forecast strengthens if interoperable implementations can carry and verify attenuated authority across different agent frameworks and tool providers; if revocation reaches descendants within measurable limits; and if auditors can reconstruct high-consequence actions without collecting excessive content. It weakens if chains are proprietary, routinely dropped at protocol boundaries, or trusted merely because they are signed even when the underlying policy was unsafe. Research should test replay, confused-deputy attacks, compromised delegates, broken clocks, partial logs and cross-organisation privacy. The initial NCCoE scope excludes external agents from untrusted sources, so enterprise demonstrations would be important evidence but not sufficient proof for open multi-party ecosystems.
FUURAA separates reported facts from editorial assessment. Partner-reported results are not treated as independent verification, and conclusions remain bounded to the named source, date, systems and disclosed operating contexts.
How to read this signal
A forward-looking synthesis, not a prediction of certainty
FUURAA has combined evidence with long-range reasoning. Readers should treat it as a question to examine, not as a statement of future fact.